Open redirect in a Python OAuth flow
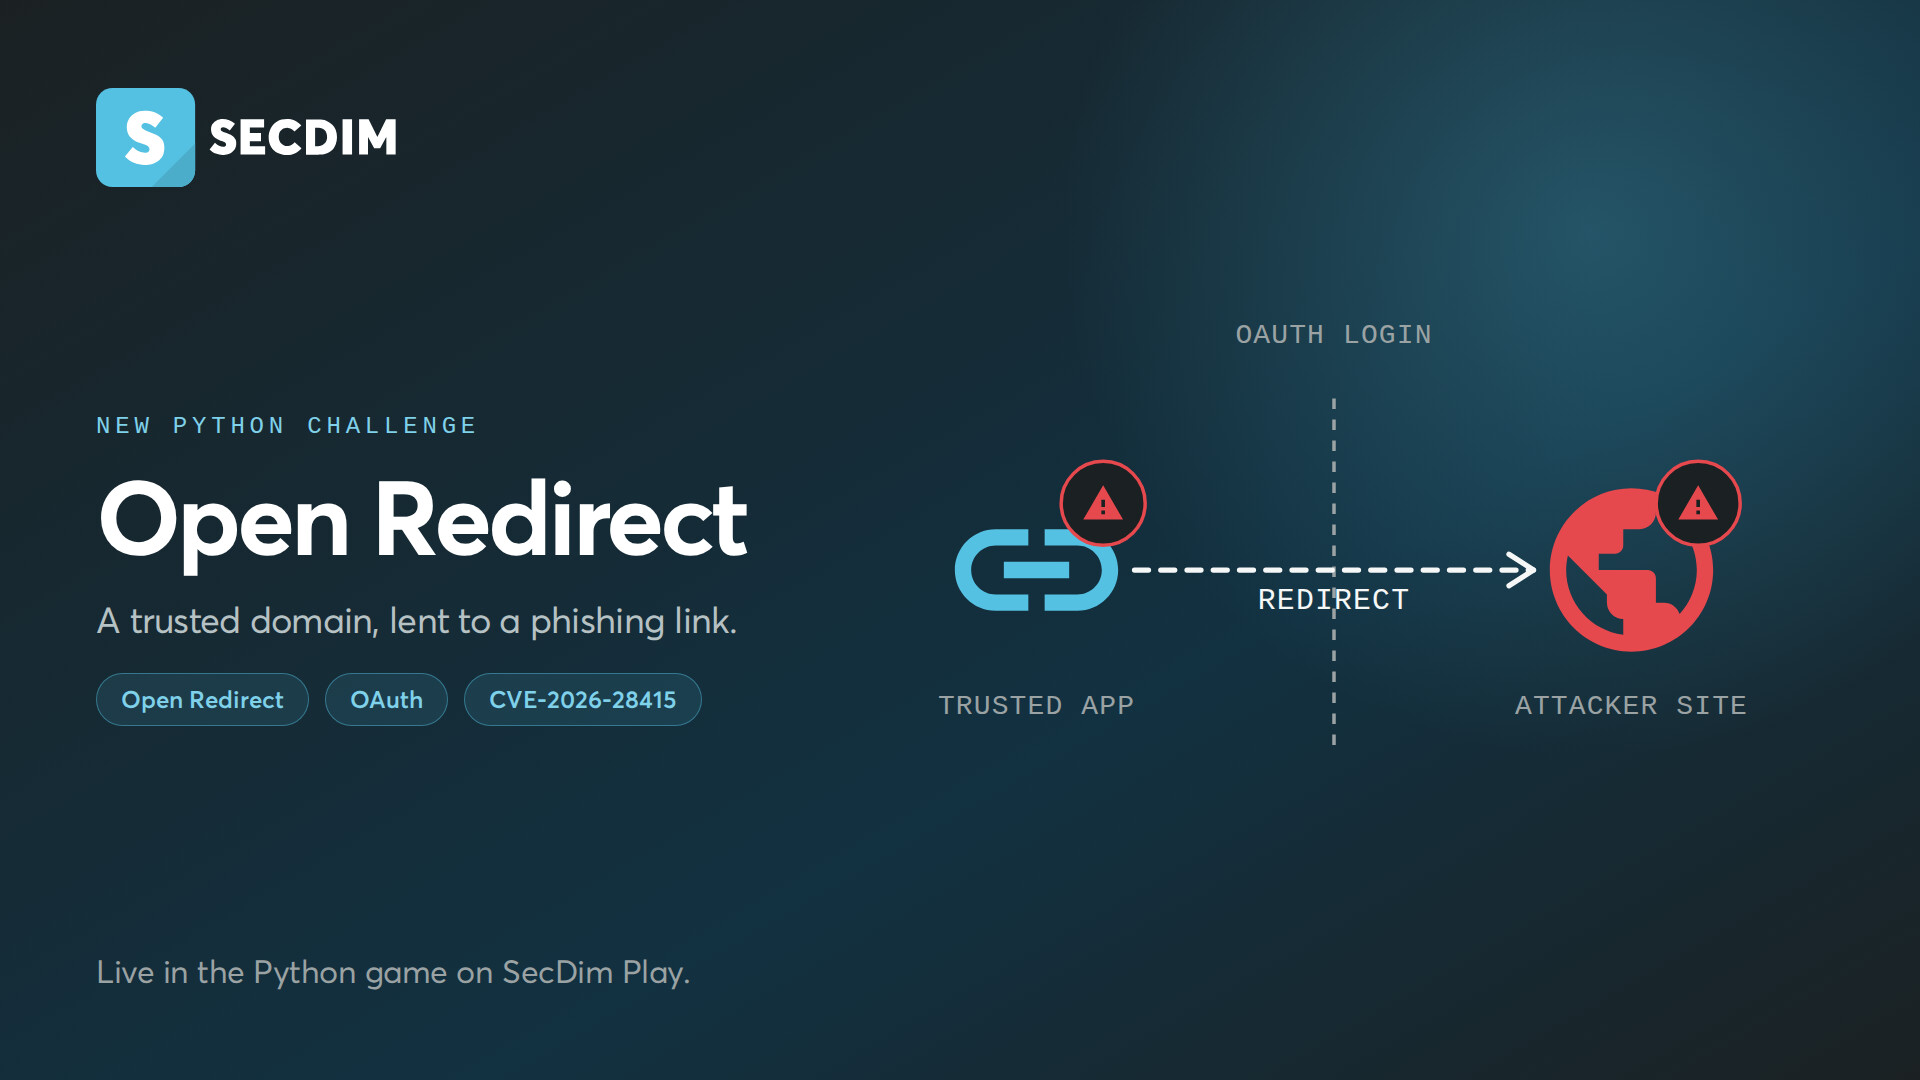
We have released a new open redirect challenge in the Python, built around an OAuth login flow.
An open redirect happens when an application sends users to a destination taken from the request without sufficient validation. After signing in, an app can send the user back to the page they started on. If that destination isn’t checked, the login flow can end on any site.
The impact is phishing: the link starts on a domain the user trusts and lands on the attacker’s.
The challenge is inspired by CVE-2026-28415, an open redirect in the OAuth login and logout endpoints of Gradio, a Python library for building machine learning demos.
Can you identify and fix the flaw?
 Play it in the Python game: Play - SecDim