
Malicious JavaScript served through Optimizely, and where CSP helps
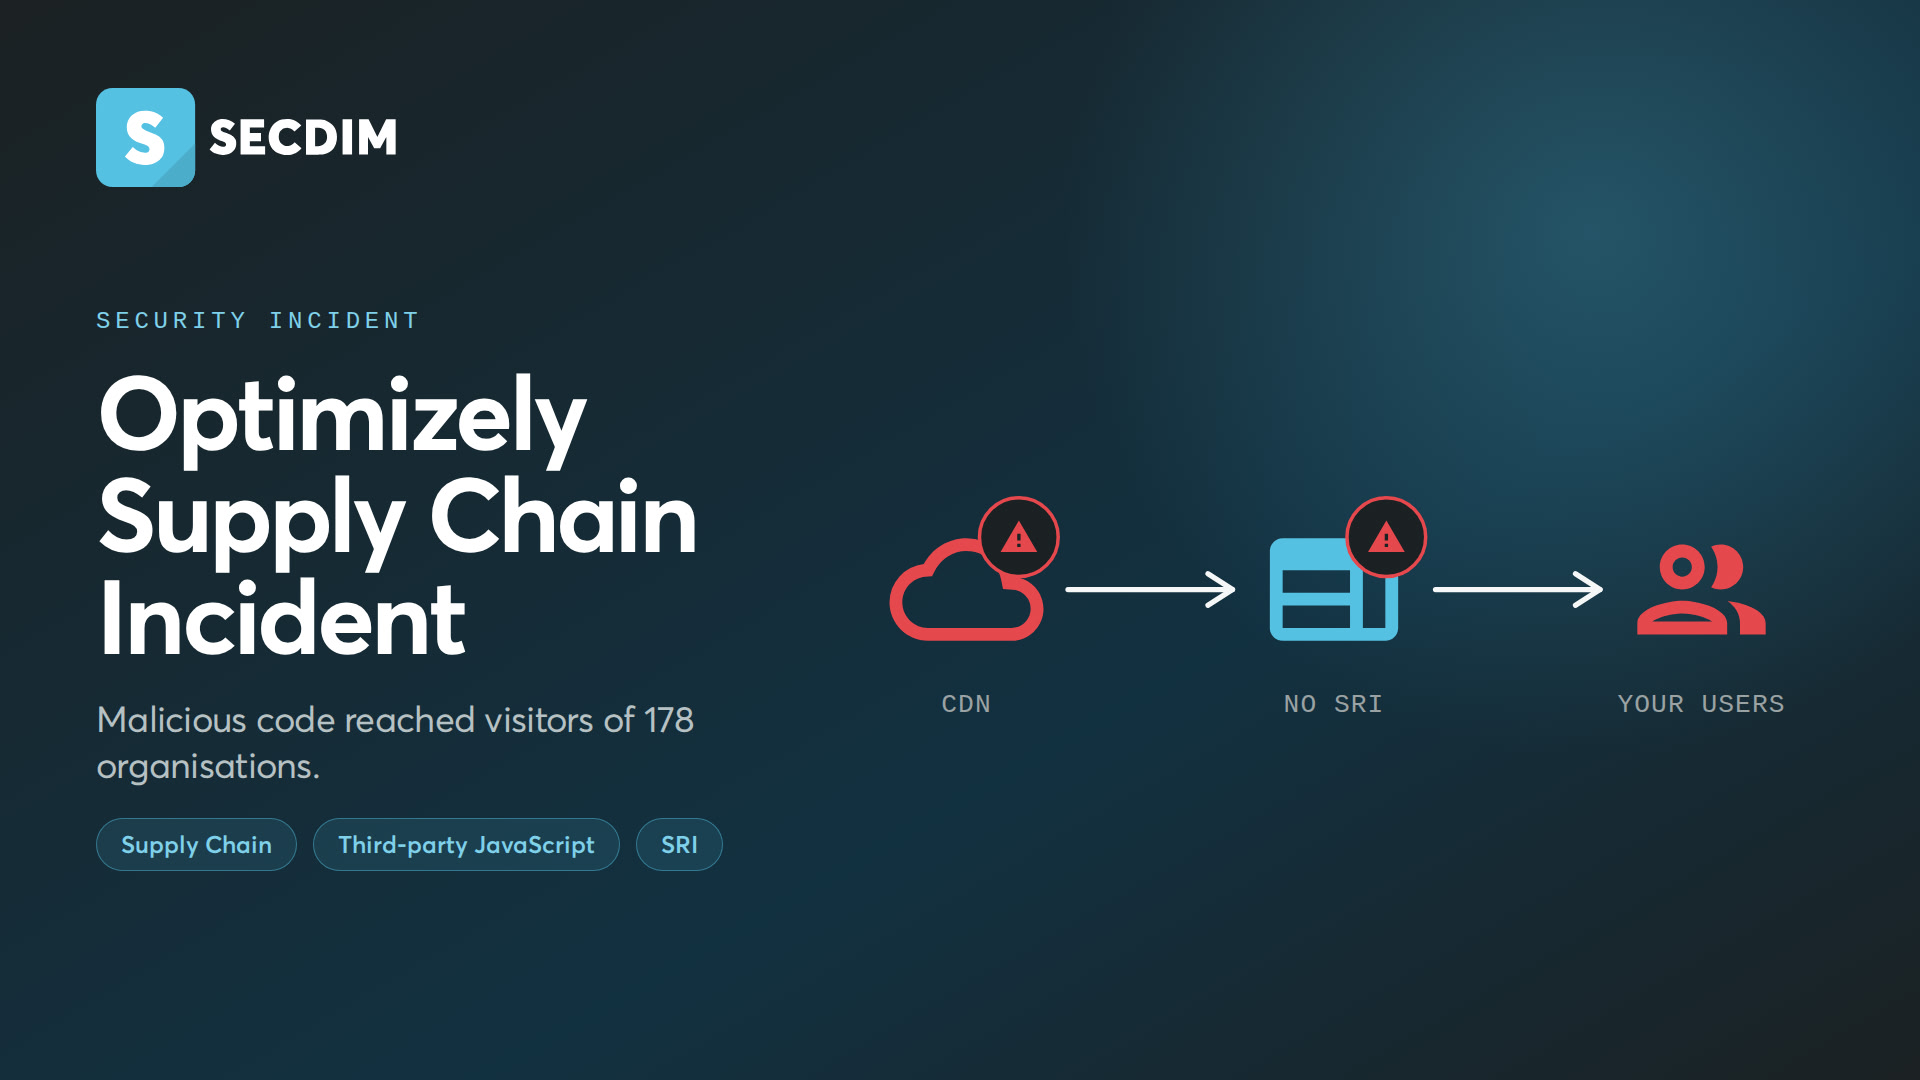
On 16 November 2026, an attacker injected malicious code into Optimizely customer projects, resulting in compromised JavaScript snippets being served through their CDN.
Report URI found the malicious code in 188 snippets belonging to 178 organisations, including BBC, CNN, Zoom and Gitlab.
The code swapped cryptocurrency wallet addresses, skimmed payment cards, sent cookies and screenshots to the attacker’s server, and loaded exploit kits on iPhones and iPads.
The affected pages loaded the script with no integrity check, so browsers ran whatever the CDN returned. Subresource Integrity (SRI) adds that check: the page states the hash of the script it expects, and the browser refuses to run a file that doesn’t match. Had these pages used SRI, the reach of this attack would have been reduced.
Our CSP.js and CSP.ts challenges are inspired by this vulnerability.
Can you Fix the Security Bug? Try it now.
 CSP.js on SecDim Play: Play - SecDim
CSP.ts on SecDim Play: Play - SecDim