
GlassWorm and a new incident response challenge
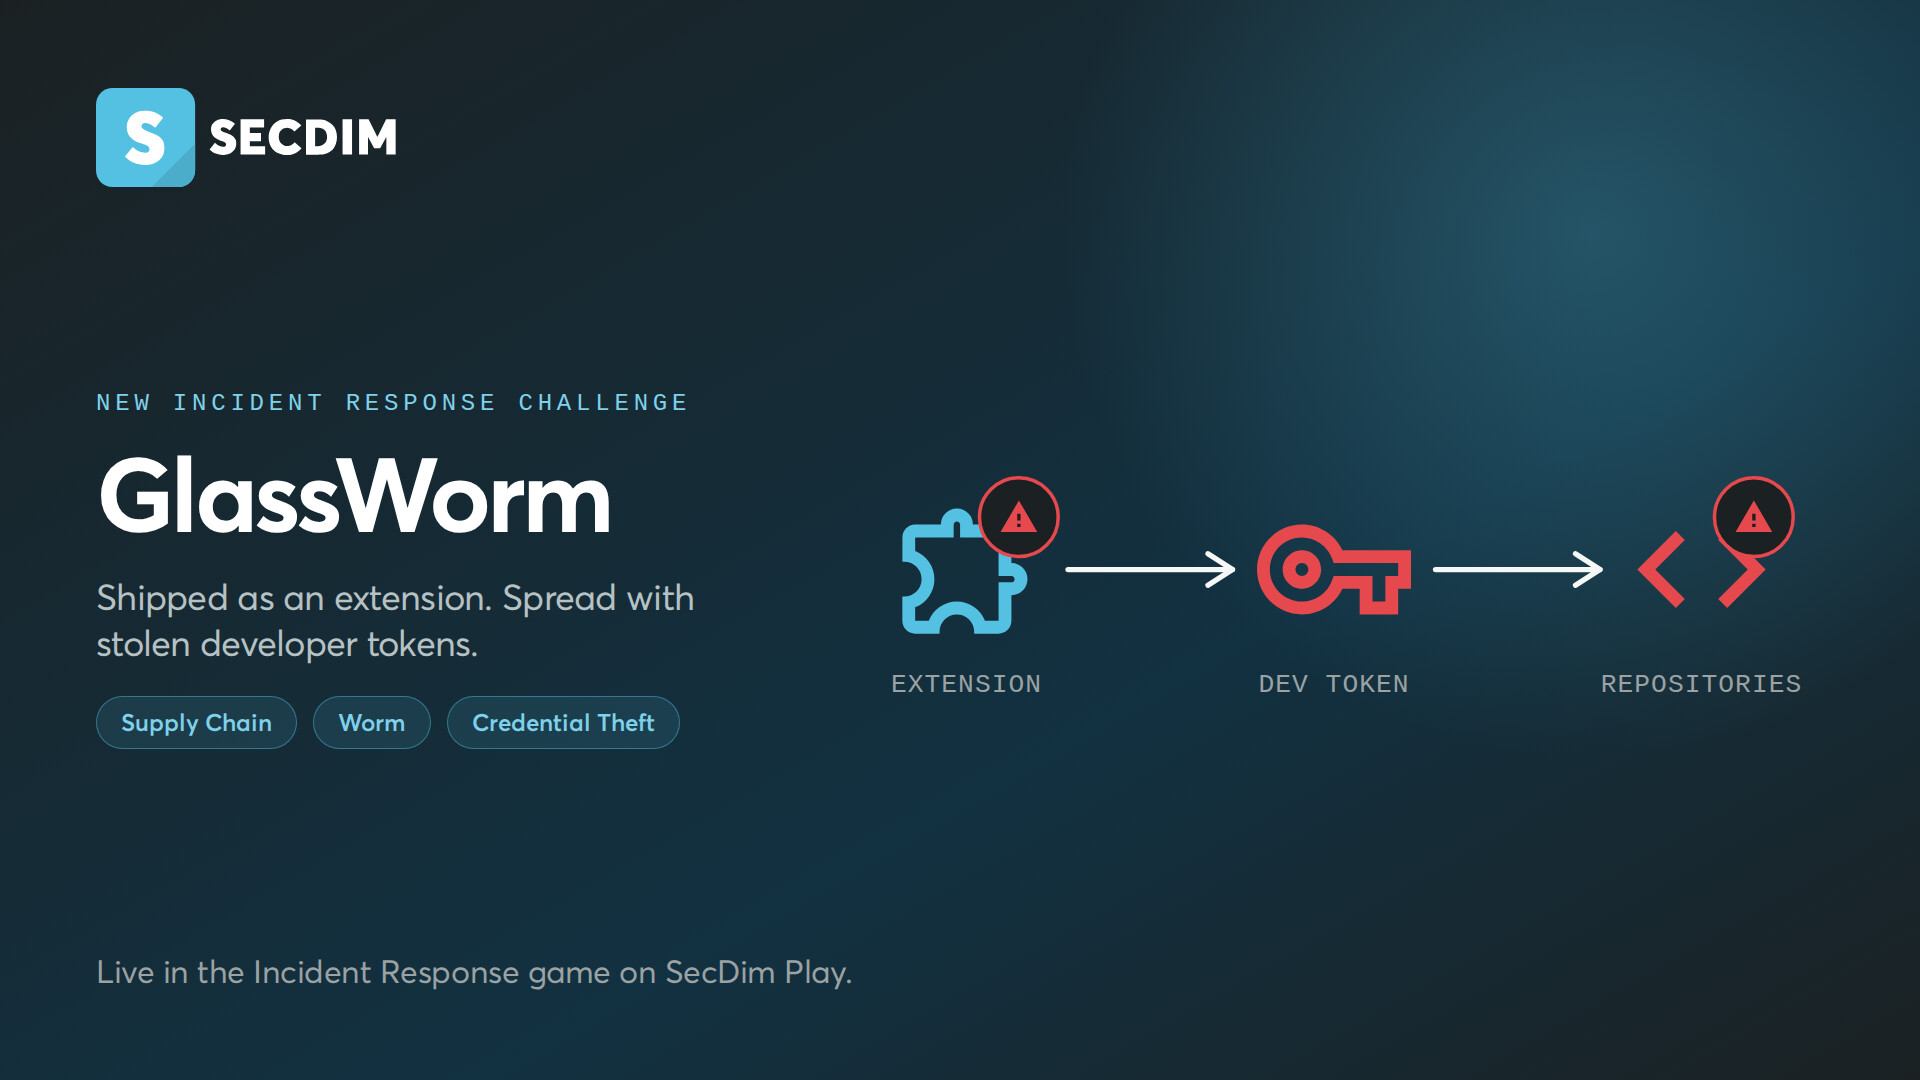
GlassWorm is a software supply-chain worm targeting developers through malicious packages and extensions.
It spreads through malicious VS Code extensions and npm packages. It has a hidden payload which, once executed, targets developer credentials, including GitHub tokens that can be used to spread the worm further.
It can also establish deeper access through a remote access trojan (RAT), targeting sensitive data such as cookies, cloud credentials and cryptocurrency wallets.
No vulnerability is exploited anywhere in that chain; instead, GlassWorm abuses compromised developer credentials and repository access to propagate.
We built a GlassWorm challenge around this incident for the Incident Response game on SecDim Play.
 GlassWorm on SecDim Play: Play - SecDim