Anushiya.cpp: a new C++ challenge inspired by PHP2Shell
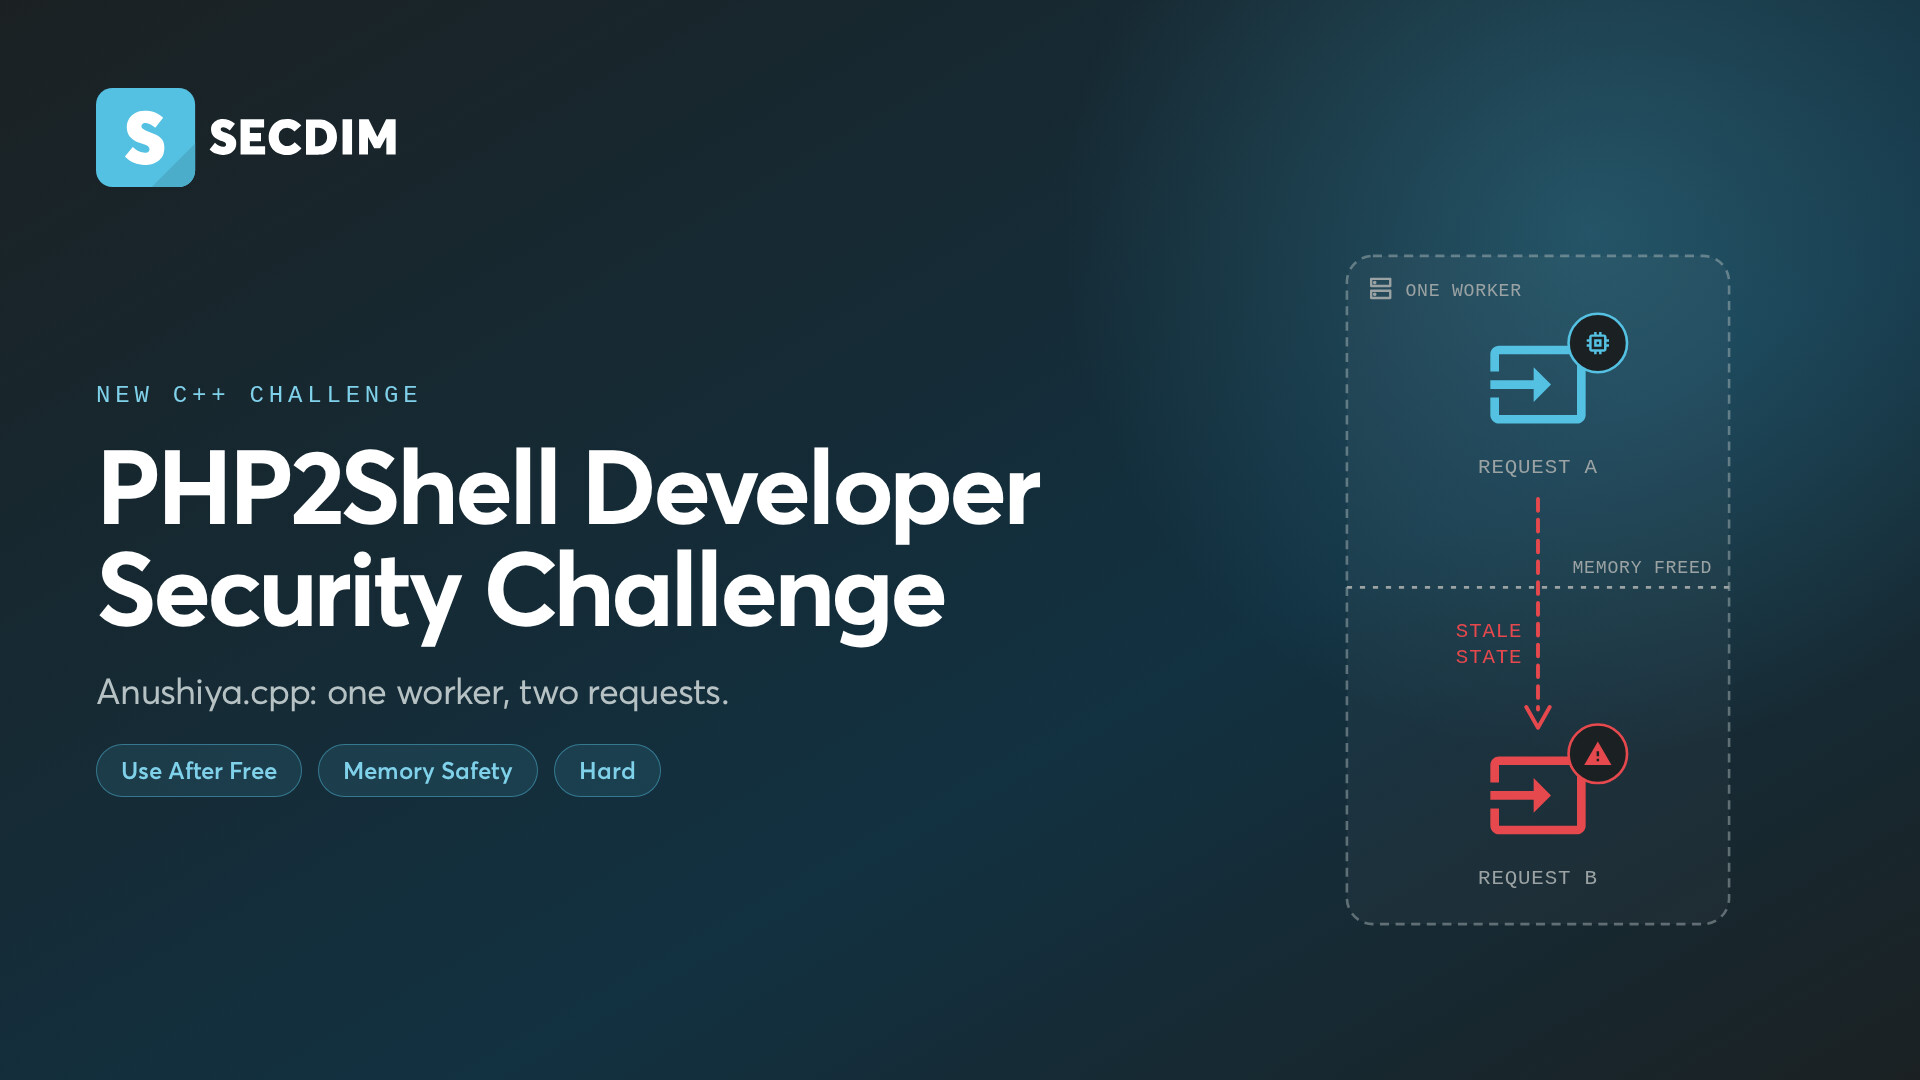
Anushiya.cpp is a new C++ challenge on SecDim Play. A process handles one request after another, and each request gets its own memory that should leave no trace once the request is done. Your job is to find the flaws in how that memory is cleaned up, and fix them.
We built it from PHP2Shell, the name given to two critical PHP vulnerabilities, CVE-2026-109618 and CVE-2026-109619. Either one can let an attacker run their own code on a server without logging in.
PHP is itself a program written in C, and it keeps one long-running process alive to serve many web requests. Both vulnerabilities come from cleanup between those requests going wrong.
In CVE-2026-109618, PHP stops a request that runs out of memory by abandoning whatever it was doing. If the request was only partly set up at that moment, PHP’s cleanup can still read the half-built data and act on it.
In CVE-2026-109619, the process holds a reference to memory that belongs to a single request. If a fatal error skips the step that clears it, that memory is released while the reference remains, and the next request handled by the same process can end up using it.
This matters beyond PHP. Any C or C++ program that manages memory by hand and handles one job after another can fail in this way, and the flaw sits in the runtime beneath the application, so correct application code does not protect you. Reading an advisory tells you what was fixed. Finding and fixing the same kind of flaw yourself teaches you where to look: the error handling and cleanup paths that only run when something has already gone wrong.
Can you identify and fix the flaws?
 Play it on SecDim Play: Play - SecDim